Hear it from Capit
I passed my SOC 2 audit on the very first try, without any findings. It was so easy.
 Brenda MurphyCEO and Founder, Humarix Solutions (Capit)
Meet Capit: a business intelligence platform built by a founder, not an IT department
Capit connects organizational intelligence with workforce intelligence. A company enters its business objectives and key financial data, and Capit returns specific recommendations, including HR objectives aligned to each business goal.
Capit is built and run by its founder, Brenda Murphy, through Humarix Solutions. There is no security team and no IT department. Brenda is not a developer, and every security decision ran through her.
Every day it runs on its own. It flags what could be out of sync, and it tells you what to do.
The problem: a new product asking customers for confidential data
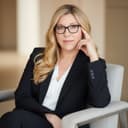
You are about to ask customers to put confidential business data into a product they have never heard of. Their first question is whether you can protect it.
Brenda Murphy knew that question was coming before any customer asked it. Capit takes in financial data and strategic objectives, so she wanted SOC 2 and a penetration test in place before launch, not after the first lost deal.
The stakes: trust before the first customer
A startup gets one first impression with each early customer. Brenda needed to:
Answer the security question with a report, not a promise
Get there without a security team or a developer background
Keep the cost workable for a pre-launch company
Why the usual options did not fit
Templates assume someone on staff knows what a control is. Consultants sell hours that a pre-launch founder cannot afford. And improvising with AI produces documents, not a program an auditor will accept.
The real goal: a program one founder can run
Passing the audit once was not enough. Brenda needed security she could keep running herself after the auditor left, with no team behind her.
How it worked: an expert directing AI
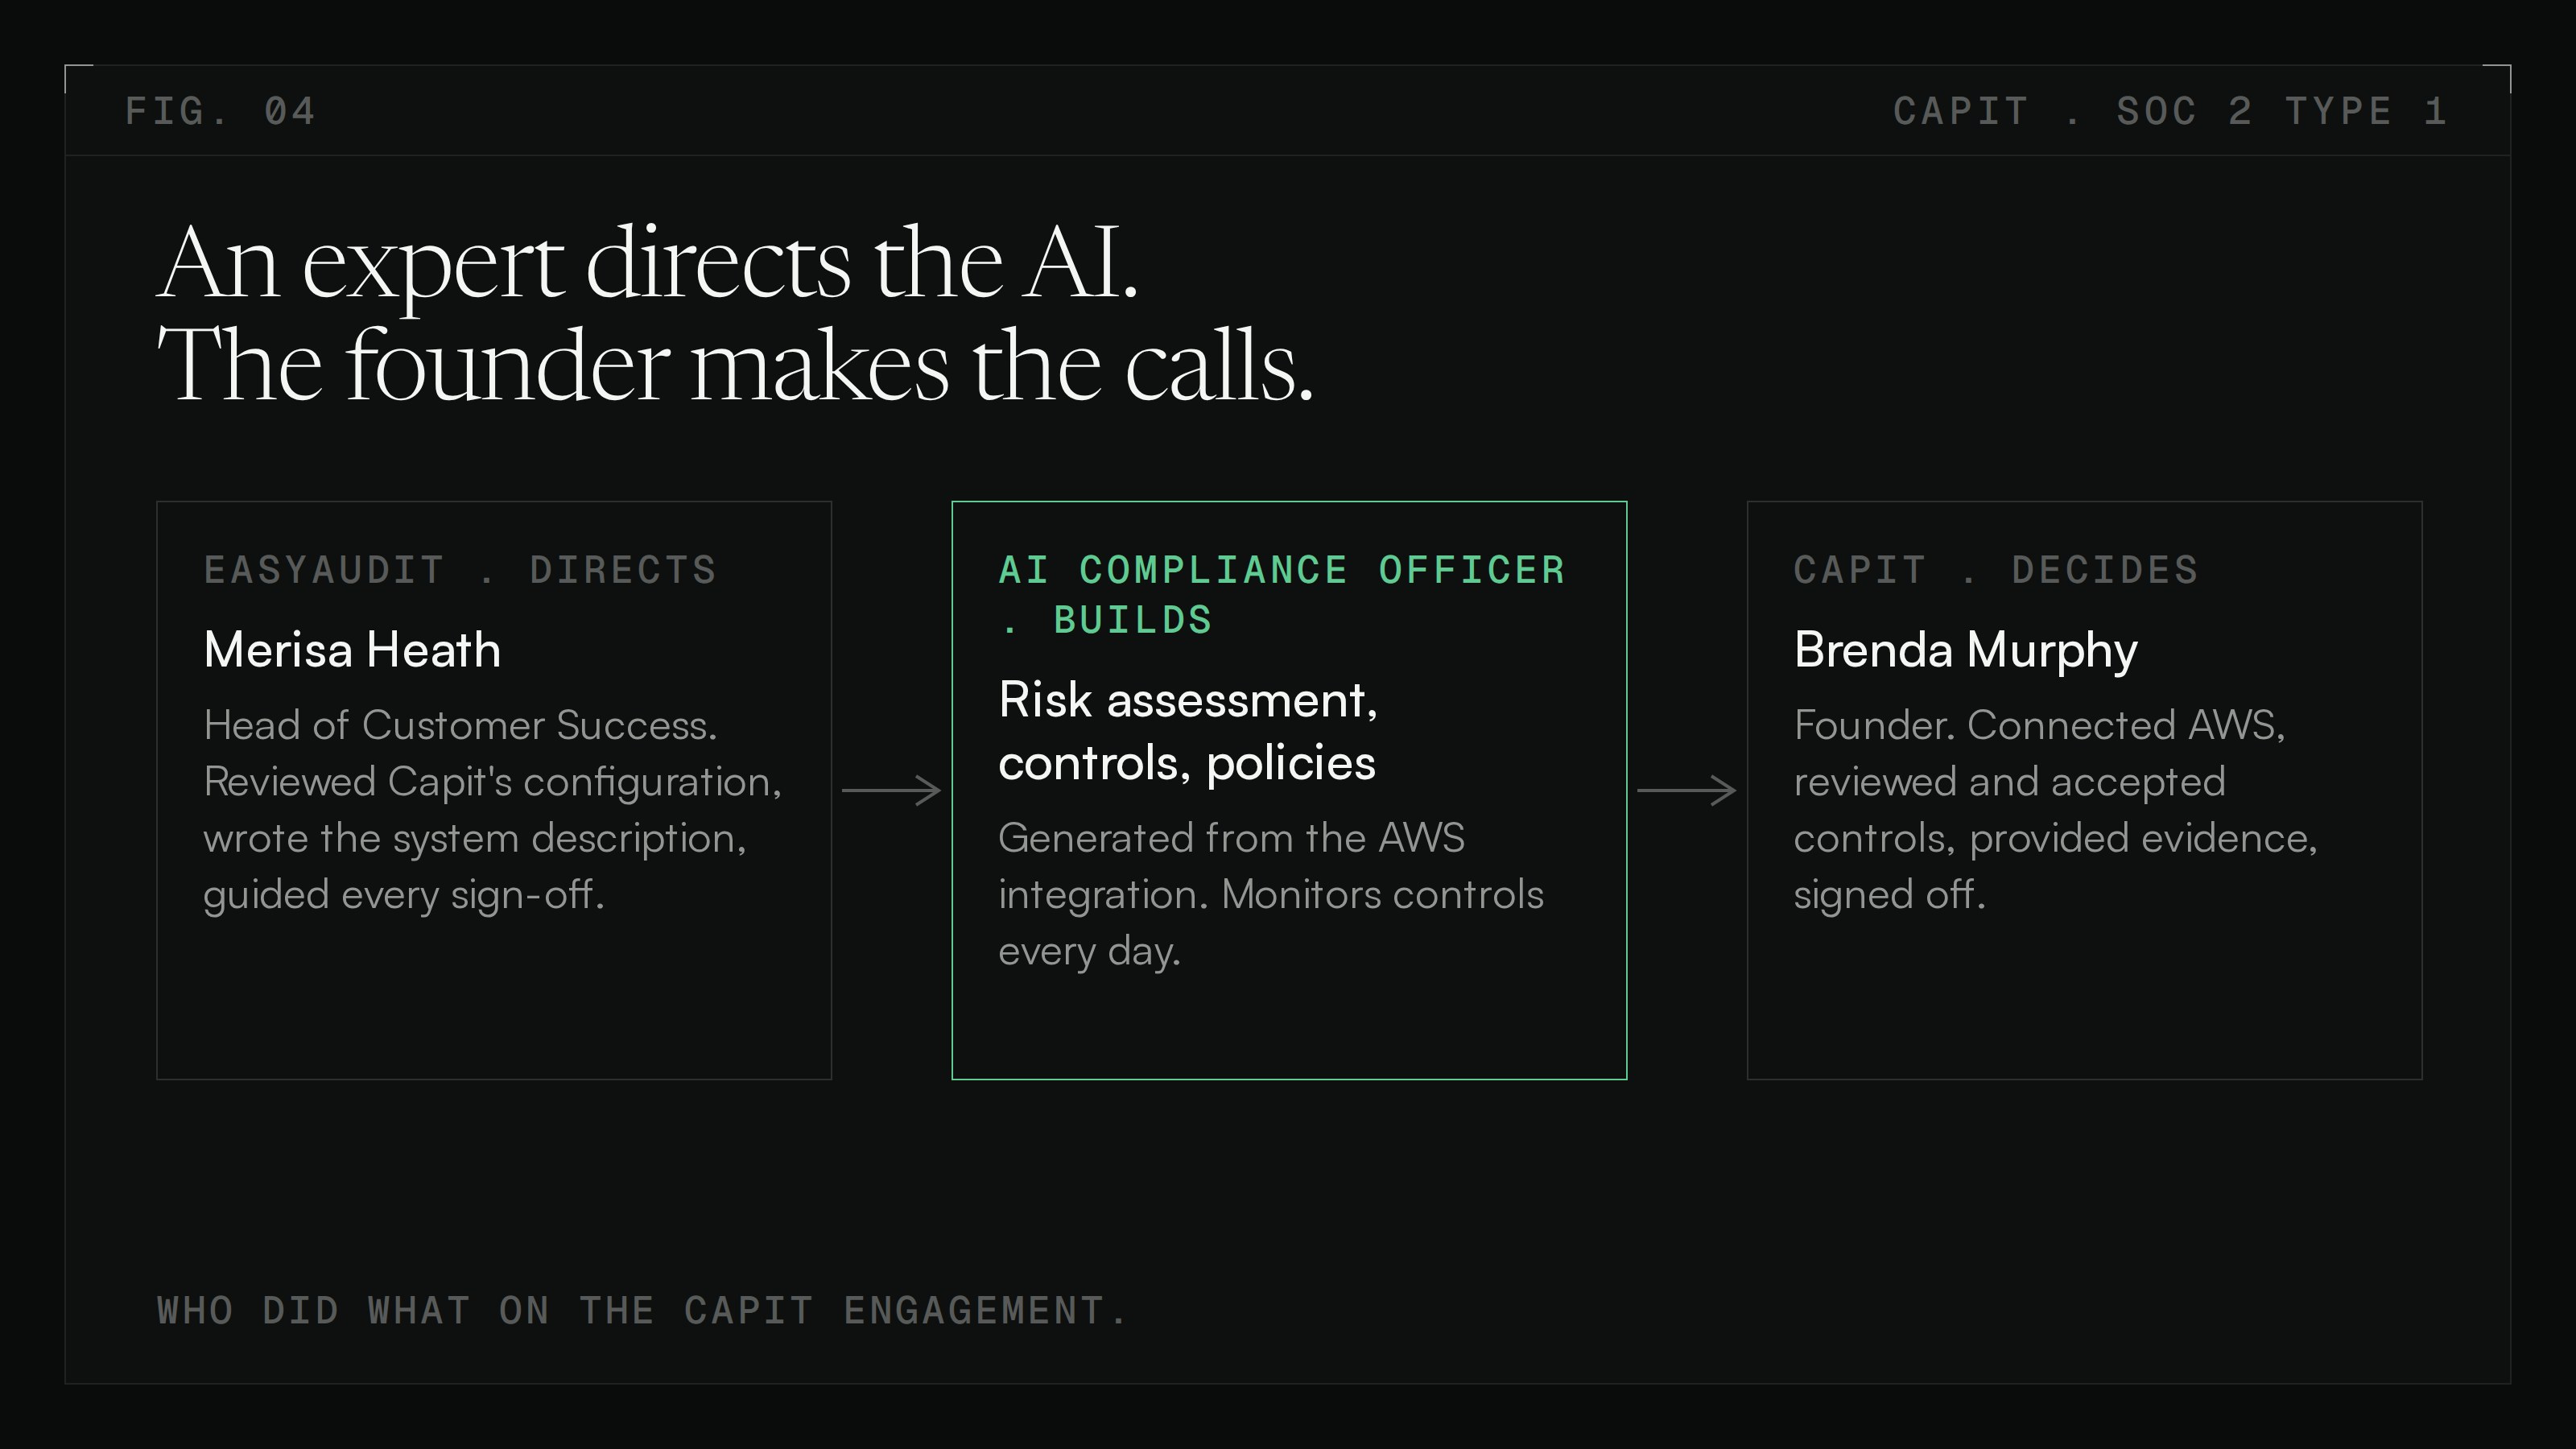
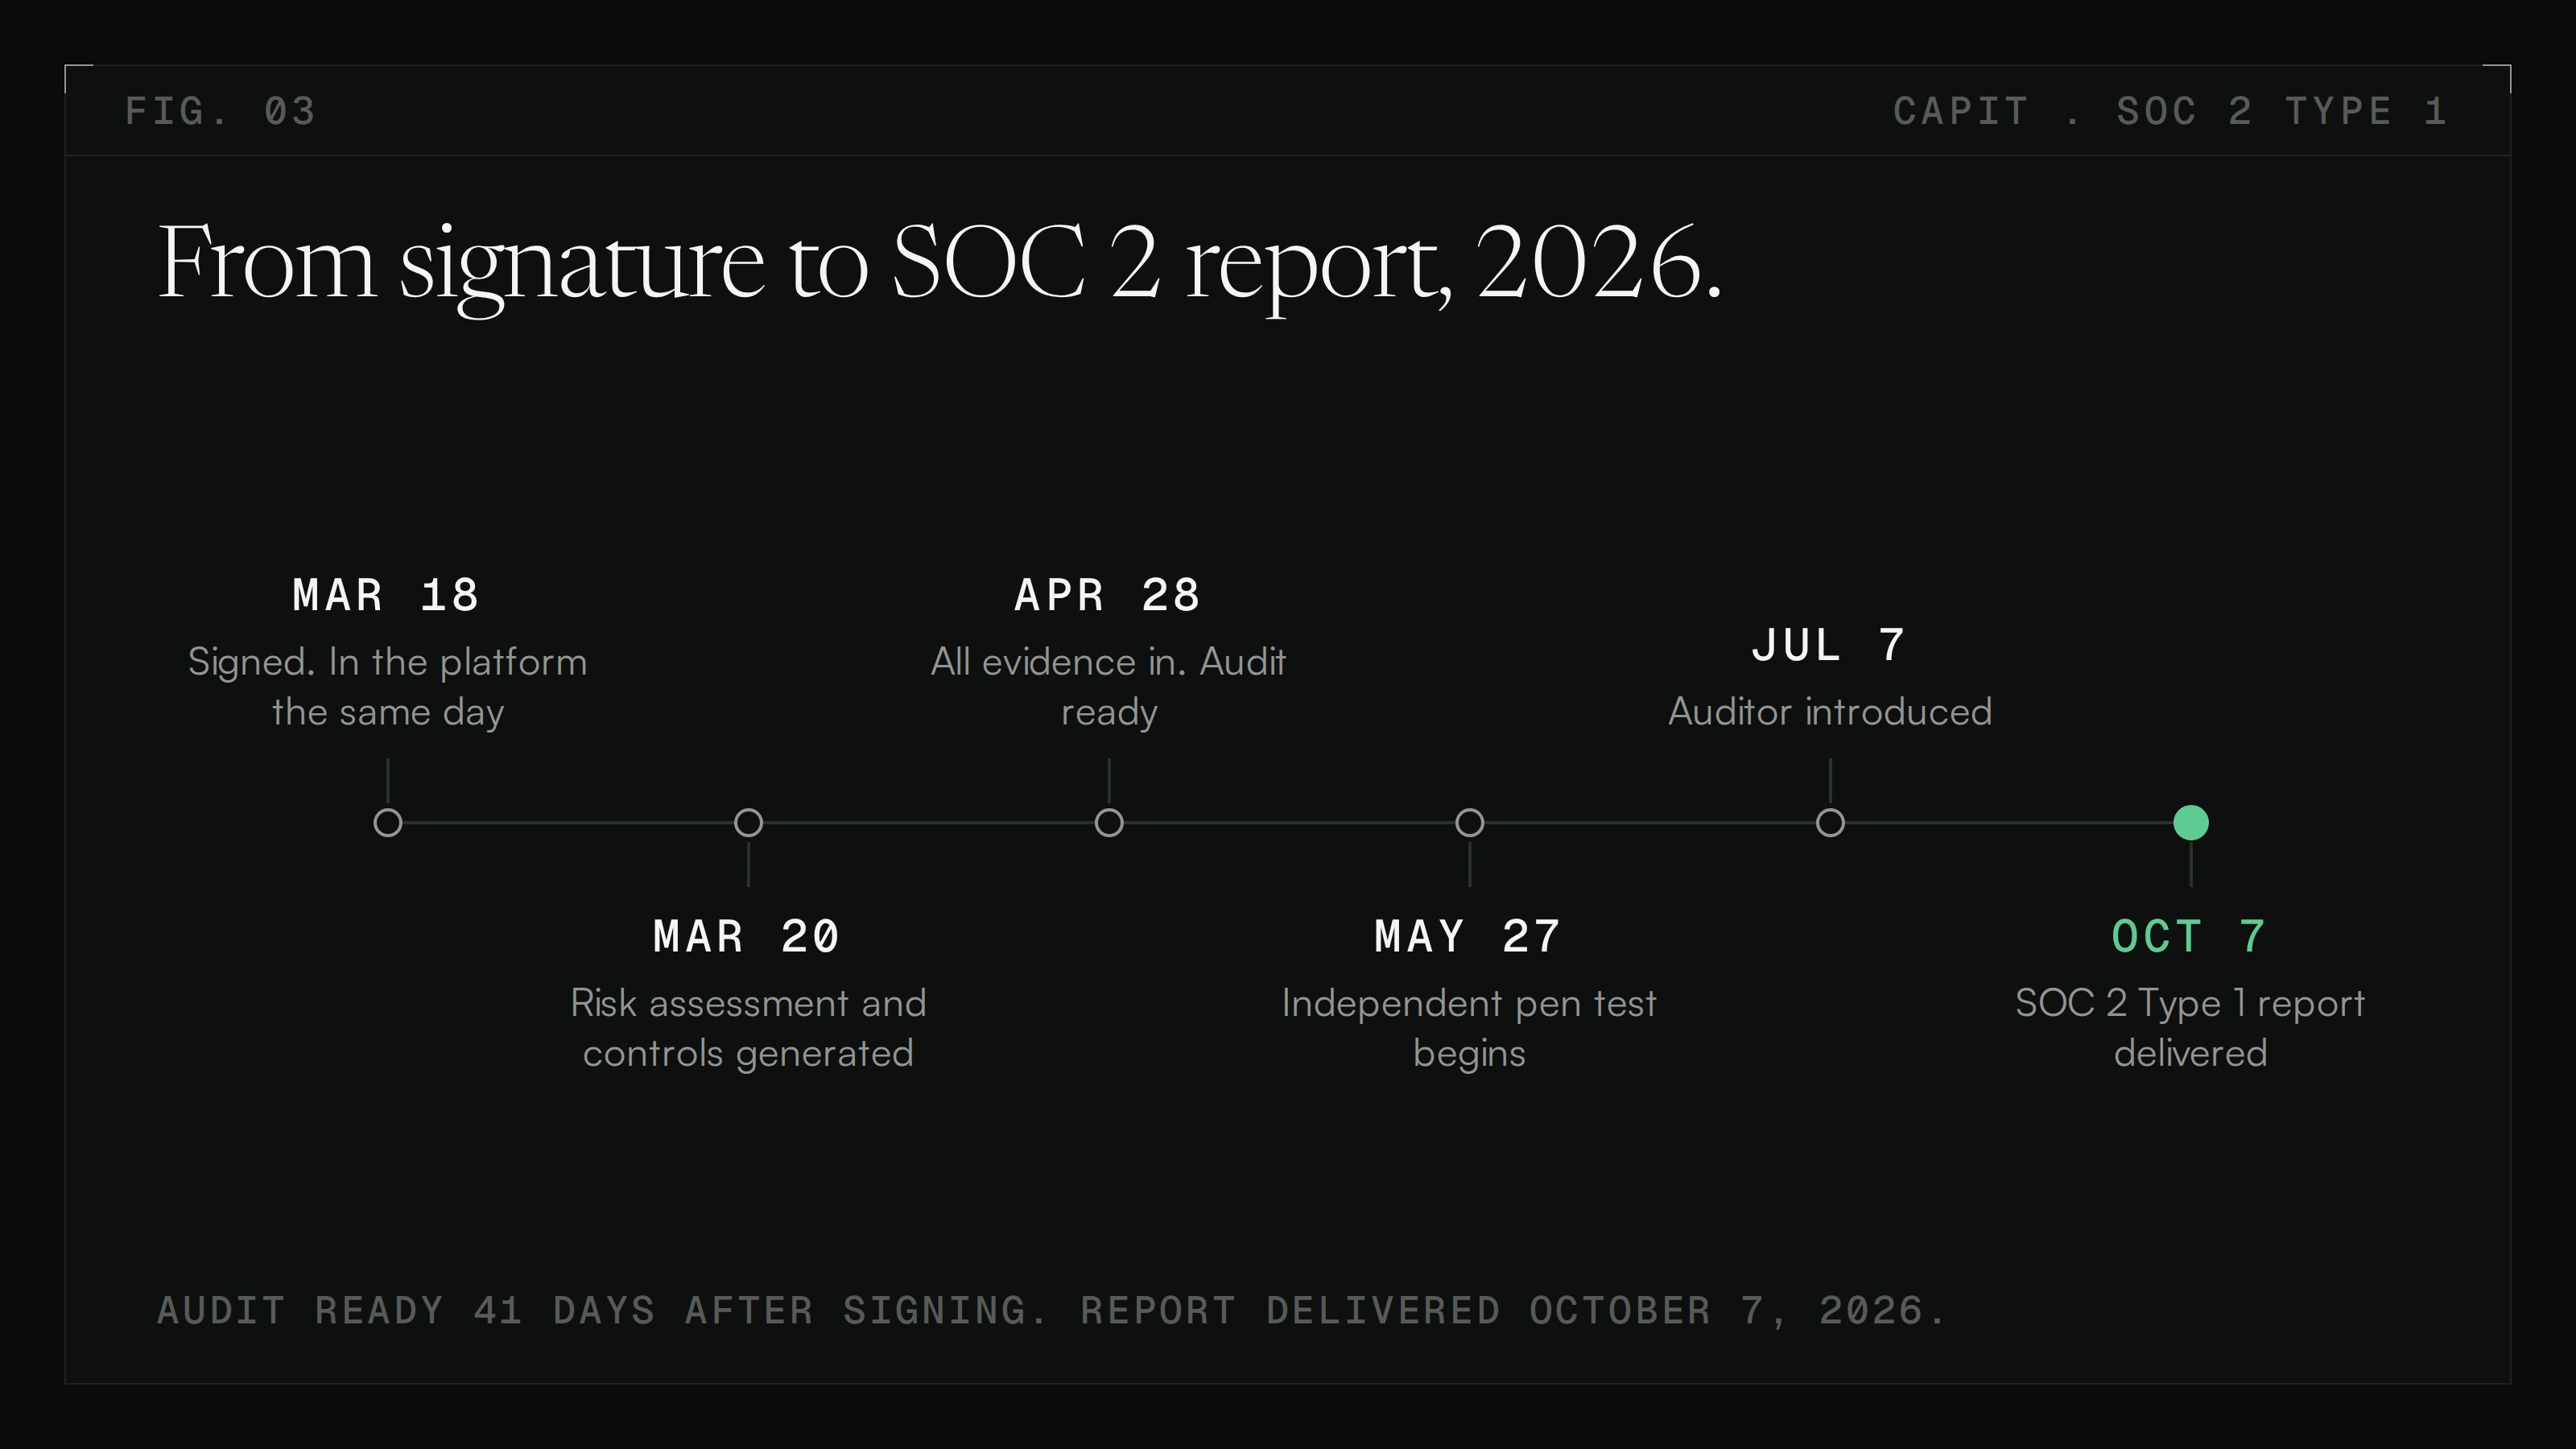
Brenda signed on March 18 and was in the platform the same day. Two days later she connected AWS, and the AI Compliance Officer generated her risk assessment and full control set.
Merisa Heath, EasyAudit’s Head of Customer Success, reviewed how Capit was configured on the back end and walked Brenda through every sign-off. When the auditor asked for a system description, Merisa wrote it without being asked.
She volunteered, put it together for me and formatted it. It was one less thing I had to do for the auditor.
Brenda MurphyCEO and Founder, Humarix Solutions (Capit)Brenda’s part was connecting her cloud account, reviewing and accepting the controls, providing evidence, and signing off. By April 28, 41 days after signing, every piece of evidence was in and Capit was audit ready.
The turning point: pen test first, then the audit
With the audit work done, Brenda made a deliberate call. She wanted an independent penetration test finished before the auditor came in.
I wanted to be pen tested before I became compliant and audited.
Brenda MurphyCEO and Founder, Humarix Solutions (Capit)EasyAudit introduced her to an independent pen testing firm. The external test ran in late May, the internal test followed, and the auditor was introduced on July 7.
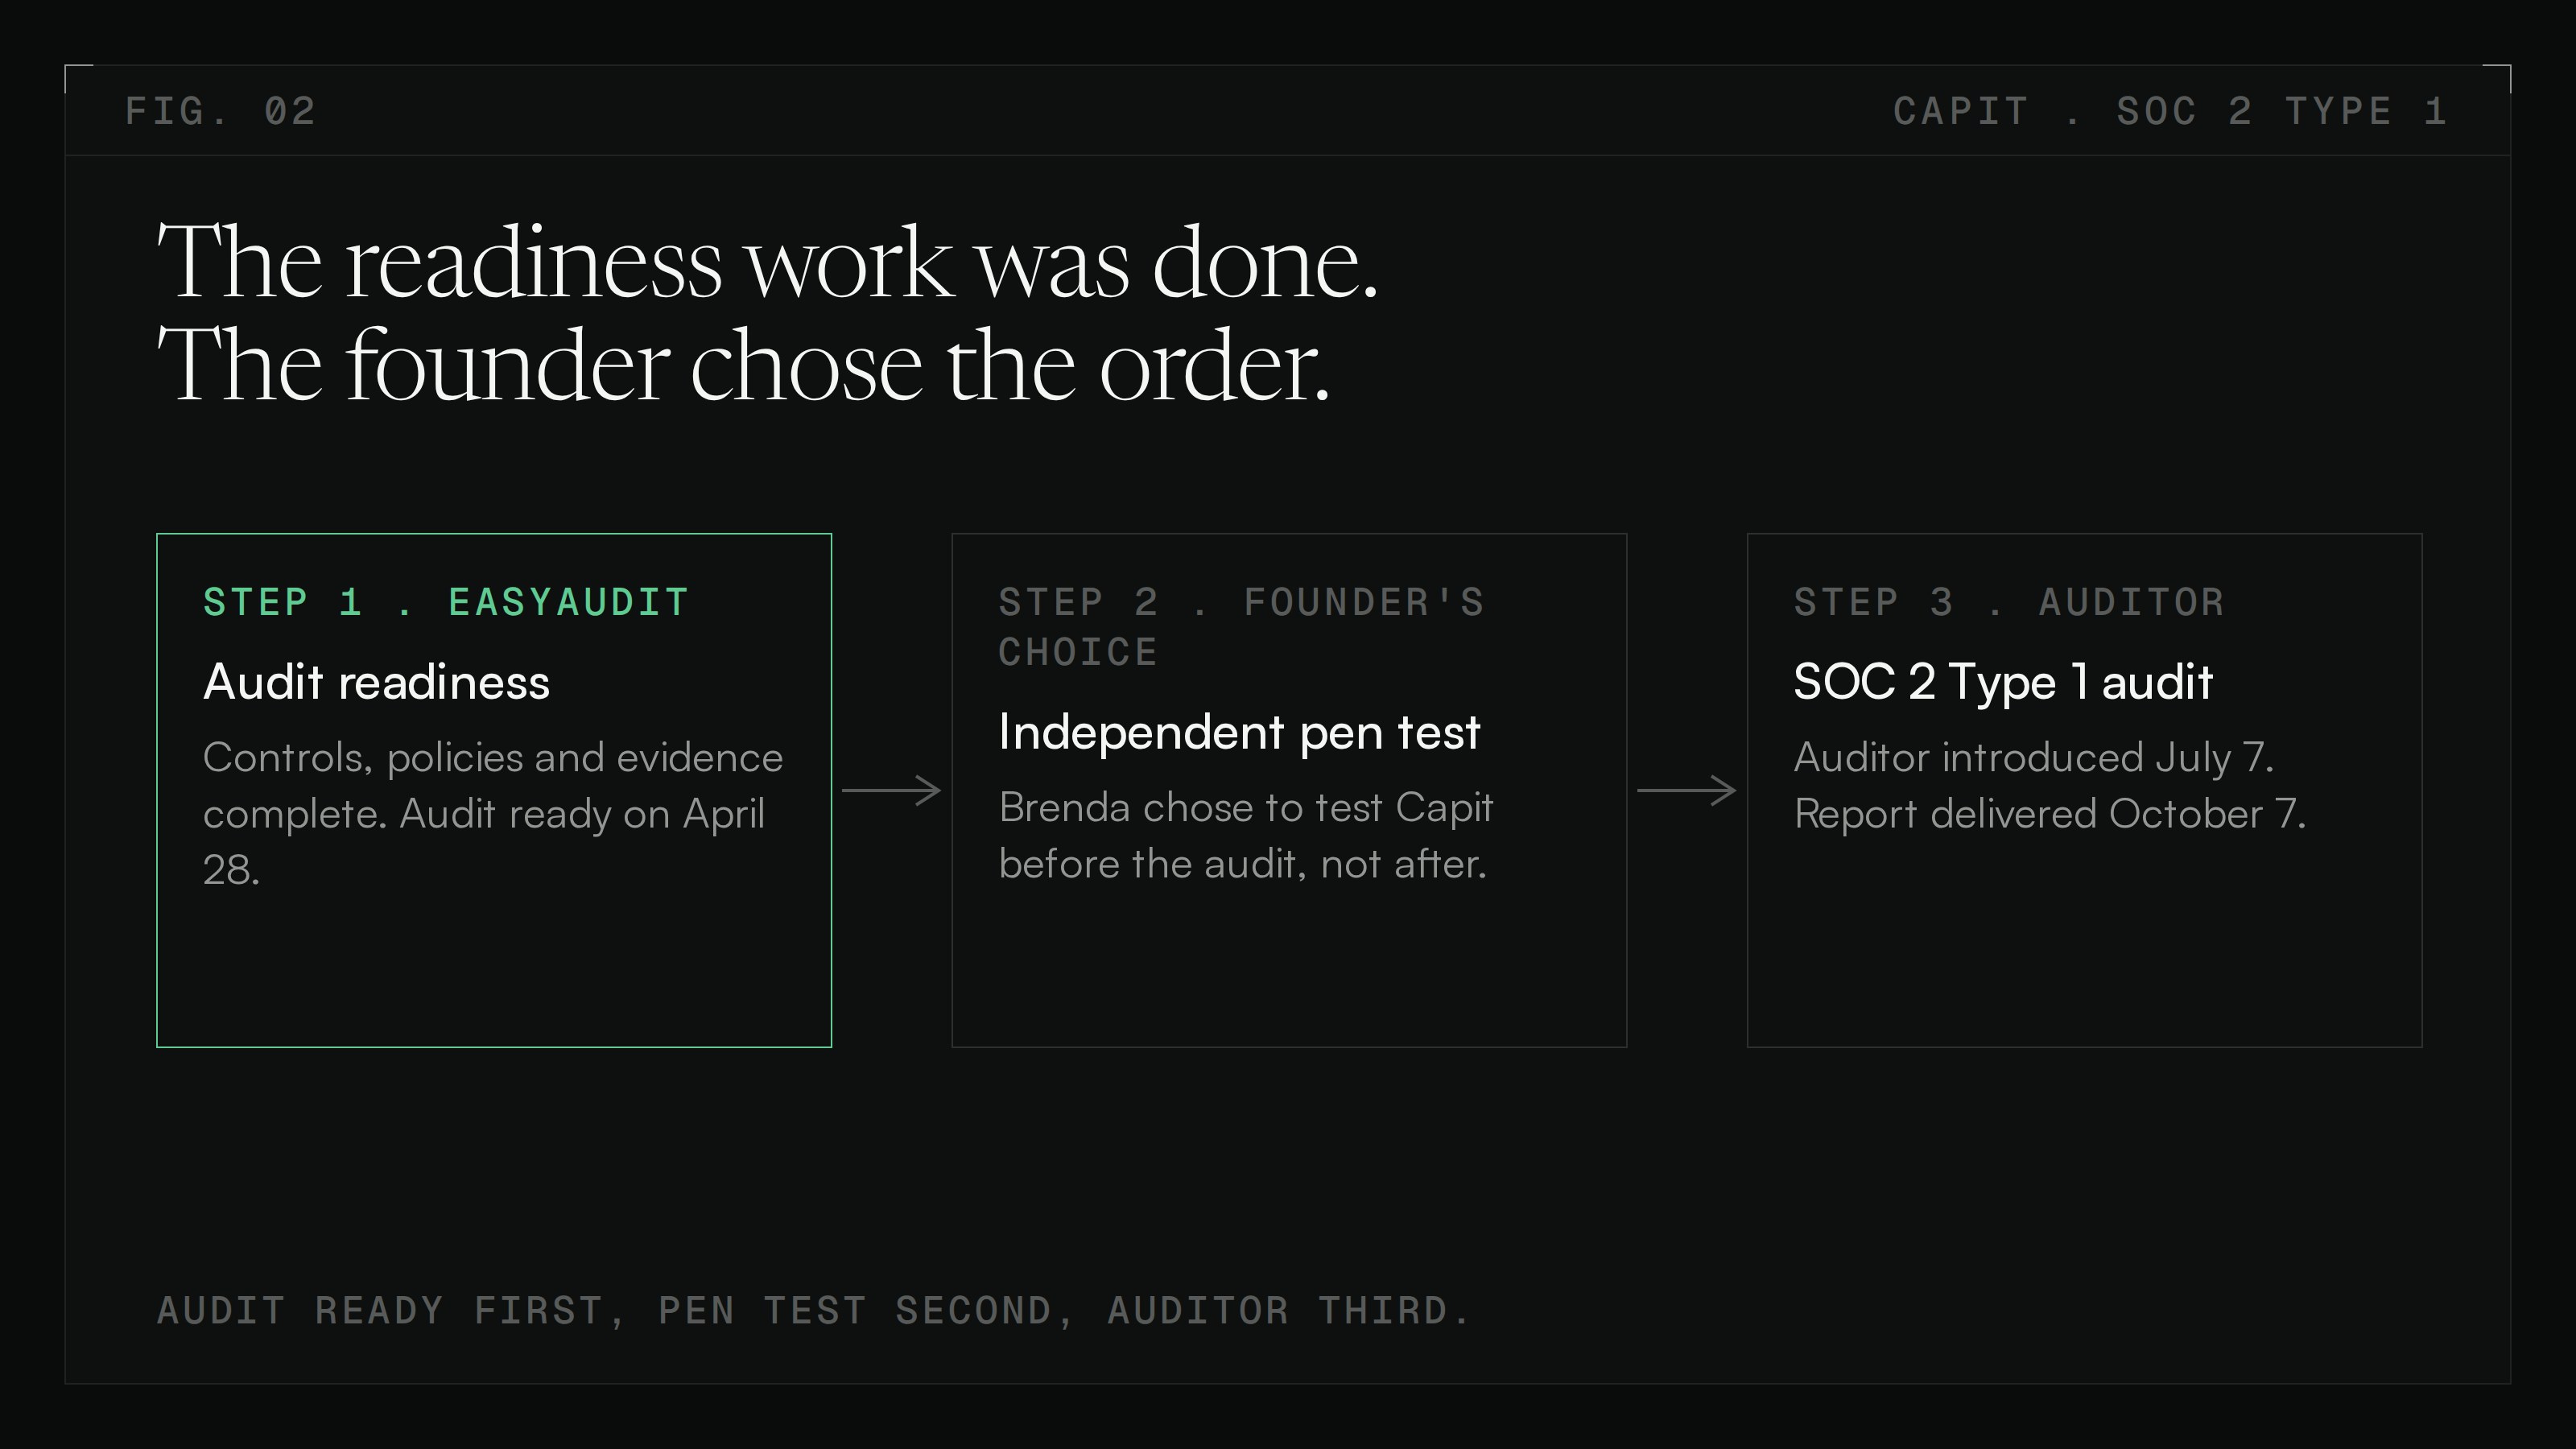
The result: SOC 2 Type 1, passed on the first try
Brenda signed the management assertion on October 7, and the final SOC 2 Type 1 report for Humarix Solutions was delivered the same day. Capit passed its first audit on the first try.
Why it worked
The platform did the building. The risk assessment and controls existed two days after signing.
An expert did the judgment. Merisa handled the work a solo founder could not, from the configuration review to the system description.
The founder kept control of the sequence. Brenda decided when to test and when to audit.
Expert direction plus AI execution equals audit ready in 41 days.
What Capit has now: security a founder can run
A SOC 2 Type 1 report to hand to any customer who asks
An independent penetration test
Daily control monitoring that flags drift and says how to fix it
An AI Compliance Officer that answers questions about Capit’s own controls
It doesn’t give you generic answers. It gives you specifics as they apply to the tool you’ve designed.
Brenda MurphyCEO and Founder, Humarix Solutions (Capit)When a prospect now asks about controls, the conversation is short.
It shuts down any doubt that you take security seriously. Most startups don’t come out of the gate SOC 2 compliant. That’s a game changer.
Brenda MurphyCEO and Founder, Humarix Solutions (Capit)Capit launched with the proof its customers would ask for already in hand.
Your customers are going to ask the same question. Start with the Compliance Simulation. It runs on your real environment, takes about 75 minutes of your time, and is free. You leave with your readiness and your gaps before you sign anything.
We do the compliance work and leave you with a program you can run, even as a team of one.